Executive Gov
  • Home
  • Acquisition & Procurement
  • Agencies
    • Department of War
    • Intelligence Community
    • DHS
    • Federal Civilian
    • Space
  • Cybersecurity
  • Technology
  • News
  • About
  • Wash100
  • Contact Us
    • Advertising
    • Submit your news
No Result
View All Result
Executive Gov
  • Home
  • Acquisition & Procurement
  • Agencies
    • Department of War
    • Intelligence Community
    • DHS
    • Federal Civilian
    • Space
  • Cybersecurity
  • Technology
  • News
  • About
  • Wash100
  • Contact Us
    • Advertising
    • Submit your news
No Result
View All Result
Executive Gov
No Result
View All Result
Home Cybersecurity

CISA Urges Federal Agencies to Protect Networks Against Apache Log4j Vulnerabilities; Jen Easterly Quoted

by Jane Edwards
December 20, 2021
in Cybersecurity, News
CISA Urges Federal Agencies to Protect Networks Against Apache Log4j Vulnerabilities; Jen Easterly Quoted

The Cybersecurity and Infrastructure Security Agency has released an emergency directive asking federal civilian agencies to mitigate Apache Log4j vulnerabilities in their internet-facing networks.

Table of Contents

  • You might also like
  • Jack Albright Named DOT Acting Chief Digital & Information Officer
  • NGA Posts Synopsis for Draft HRM II Human Resources Support RFP
  • Contractors Seek DCSA Metrics on Continuous Vetting

You might also like

Jack Albright Named DOT Acting Chief Digital & Information Officer

NGA Posts Synopsis for Draft HRM II Human Resources Support RFP

Contractors Seek DCSA Metrics on Continuous Vetting

CISA said Friday multiple threat actors are exploiting a series of vulnerabilities in the Java-based logging library Log4j, allowing hackers to remotely execute code on a server.

The agency issued the emergency directive based on several reasons, including the exploitation of such vulnerabilities in external network environments, prevalence of affected software in federal networks and the potential impact of a successful breach.

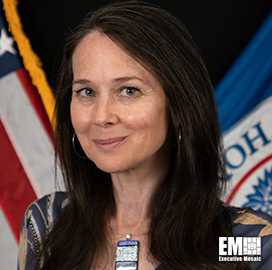
“The log4j vulnerabilities pose an unacceptable risk to federal network security,” said CISA Director Jen Easterly. 

“CISA also strongly urges every organization large and small to follow the federal government’s lead and take similar steps to assess their network security and adapt the mitigation measures outlined in our Emergency Directive. If you are using a vulnerable product on your network, you should consider your door wide open to any number of threats,” added Easterly.

The directive requires agencies to enumerate all solution stacks accepting data input from the internet and assess all software assets in identified solution stacks against the CISA-managed GitHub repository, among other actions, by Dec. 23.

By Dec. 28, agencies should report all affected software applications and related assets and confirm with CISA that their internet-accessible IP addresses are updated.

CISA has established a webpage to provide network defenders information on Log4j mitigation measures and other resources. The platform also includes a GitHub repository of affected services and devices.
Stay connected via Google News
Follow us for the latest travel updates and guides.
Add as preferred source on Google
Share5Tweet19
Previous Post

DISA to Sunset milCloud 2.0 Contract in May

Next Post

Maj. Gen. Davis Nominated Air Force Inspector General

Recommended For You

Navy Commissions USS Manchester in Portsmouth, N.H.

by Nichols Martin
May 29, 2018
Navy Commissions USS Manchester in Portsmouth, N.H.

The U.S. Navy has commissioned the USS Manchester, or LCS 14, at a ceremony Saturday in Portsmouth, N.H., USNI News reported Monday. The addition of the newest Independence-class littoral combat ship raises the...

Read moreDetails

Christine Wormuth to Step Down as DoD Undersecretary for Policy in June

by Jane Edwards
April 25, 2016
Christine Wormuth to Step Down as DoD Undersecretary for Policy in June

Christine Wormuth Christine Wormuth, undersecretary for policy at the Defense Department, will leave her current position in June after more than seven years of service under the current administration. Defense Secretary...

Read moreDetails

Novetta Recognized for National Security Efforts Under NCIS RISER Program; Bill Dorr, Kevin Heald Quoted

by Sarah Sybert
March 28, 2023
Novetta Recognized for National Security Efforts Under NCIS RISER Program; Bill Dorr, Kevin Heald Quoted

Novetta has been recognized by the Naval Criminal Investigative Service (NCIS) Technical Services Field Office Identity Activities Branch (TSFO-IA) for the company’s contributions to the RISER Program, which...

Read moreDetails

TransUnion Study Shows Prevalence of Account Takeover Fraud in Public Sector; Jonathan McDonald Quoted

by Jane Edwards
June 17, 2021
Jonathan McDonald

A study conducted by TransUnion and the Ponemon Institute has found that 53 percent of federal, state and local government agency leaders said they have seen an increase...

Read moreDetails

Leidos Anticipates Adoption of NCMA Contract Management Standard; Kim Denver Quoted

by Ireland Degges
June 1, 2023
Kim Denver

Leidos plans to align with the National Contract Management Association’s Contract Management Standard. The process will involve setting workforce competency requirements that meet the American National Standards Institute-approved guidelines, the...

Read moreDetails
Sign Up For Our Newsletter
Subscribe to our mailing list to receives daily updates direct to your inbox!
Invalid email address
Your privacy is guranteed.
Thanks for subscribing!

Sponsors

About ExecutiveGov

ExecutiveGov, published by Executive Mosaic, is a site dedicated to the news and headlines in the federal government. ExecutiveGov serves as a news source for the hot topics and issues facing federal government departments and agencies such as Gov 2.0, cybersecurity policy, health IT, green IT and national security. We also aim to spotlight various federal government employees and interview key government executives whose impact resonates beyond their agency.

CATEGORIES

  • Acquisition & Procurement
  • Announcements
  • Articles
  • Artificial Intelligence
  • Australia
  • Awards
  • Big Data & Analytics News
  • C4ISR
  • C5ISR
  • Cloud
  • Contract Awards
  • Cybersecurity
  • Defense And Intelligence
  • Defense Security Cooperation
  • Department of War
  • DHS
  • Digital Assets
  • Digital Modernization
  • Events
  • Executive Moves
  • Executive Spotlights
  • Federal Civilian
  • Financial Reports
  • Foreign Military Sales
  • General News
  • GovCon Expert
  • Government Cloud
  • Government Technology
  • GSA
  • Healthcare IT
  • Industry News
  • Intelligence Community
  • Legislation
  • M&A Activity
  • Middle East
  • National Security
  • News
  • Policy Updates
  • Press Releases
  • Profiles
  • Space
  • Technology
  • Videos
  • Wash100
Sign Up For Our Newsletter
Subscribe to our mailing list to receives daily updates direct to your inbox!
Invalid email address
Your privacy is guranteed.
Thanks for subscribing!

Copyright 2026 Executive Mosaic. All Rights Reserved. Site Archive

No Result
View All Result
  • Home
  • Acquisition & Procurement
  • Agencies
    • Department of War
    • Intelligence Community
    • DHS
    • Federal Civilian
    • Space
  • Cybersecurity
  • Technology
  • News
  • About
  • Wash100
  • Contact Us
    • Advertising
    • Submit your news

Copyright 2026 Executive Mosaic. All Rights Reserved. Site Archive

Get your free GovCon news!

Get your latest GovCon news and insights. Become a VIP and subscribe to the GovConWire Daily News.

Invalid email address
We promise not to spam you. You can unsubscribe at any time.
Thanks for subscribing!