Executive Gov
  • Home
  • Acquisition & Procurement
  • Agencies
    • Department of War
    • Intelligence Community
    • DHS
    • Federal Civilian
    • Space
  • Cybersecurity
  • Technology
  • News
  • About
  • Wash100
  • Contact Us
    • Advertising
    • Submit your news
No Result
View All Result
Executive Gov
  • Home
  • Acquisition & Procurement
  • Agencies
    • Department of War
    • Intelligence Community
    • DHS
    • Federal Civilian
    • Space
  • Cybersecurity
  • Technology
  • News
  • About
  • Wash100
  • Contact Us
    • Advertising
    • Submit your news
No Result
View All Result
Executive Gov
No Result
View All Result
Home Cybersecurity

CISA Orders Federal Agencies to Mitigate Critical Cisco SD-WAN Threats

by Miles Jamison
February 26, 2026
in Cybersecurity, News
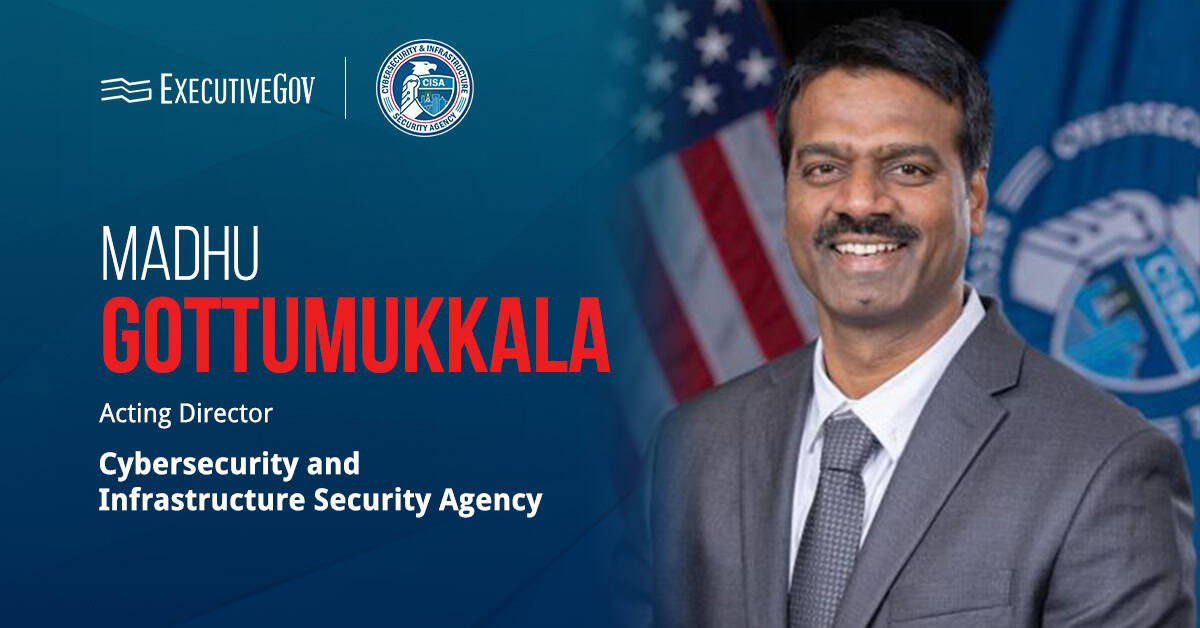
CISA Acting Director Madhu Gottumukkala. CISA released emergency directives to agencies to mitigate Cisco SD-WAN threats.

CISA released Emergency Directive 26-03 and Supplemental Direction ED 26-03 to address threats targeting federal networks using designated Cisco systems and software.

The Cybersecurity and Infrastructure Security Agency has released Emergency Directive 26-03, Mitigate Vulnerabilities in Cisco SD-WAN Systems, along with Supplemental Direction ED 26-03, Hunt and Hardening Guidance for Cisco SD-WAN Systems, to address threat actors actively targeting federal networks leveraging designated Cisco systems and software.
Table of Contents

    • You might also like
    • Army Forms PM ATSR to Unify Aerial, Ground Sensor Acquisitions
    • DOJ Stands Up Super Intelligence Task Force to Counter AI Misuse
    • DOW Commits $150M Conditional Loan to LeoLabs to Scale Space Radar Production
  • What Prompted the 26-03 Directive?
  • What Actions Must Agencies Take in Response to 26-03?
  • Previous Cisco-Related Emergency Action

You might also like

Army Forms PM ATSR to Unify Aerial, Ground Sensor Acquisitions

DOJ Stands Up Super Intelligence Task Force to Counter AI Misuse

DOW Commits $150M Conditional Loan to LeoLabs to Scale Space Radar Production

CISA Orders Federal Agencies to Mitigate Critical Cisco SD-WAN Threats

The Potomac Officers Club’s 2026 Cyber Summit on May 21 will examine how government and industry are responding to escalating global cyber threats similar to the attacks on Cisco SD-WAN Systems. Sign up now to join this important GovCon event!

What Prompted the 26-03 Directive?

CISA said Wednesday the identified flaws pose an unacceptable risk to federal civilian executive branch networks, prompting immediate remediation. The company’s forensic analysis, conducted in coordination with international partners, determined that the vulnerabilities could be exploited with limited complexity.

What Actions Must Agencies Take in Response to 26-03?

Agencies are required to create a comprehensive inventory of all affected Cisco SD-WAN assets, collect relevant system logs and virtual snapshots, and apply patches addressing CVE-2026-20127 and CVE-2022-20775. In addition, organizations should actively search their environments for signs of compromise and follow the security measures detailed in Cisco’s Catalyst SD-WAN Hardening Guide. The agency issued an alert accompanied by joint guidance titled the Cisco SD-WAN Threat Hunt Guide to help network defenders identify and respond to malicious activity.

“Operational disruptions create strain and uncertainty, give our adversaries unnecessary advantages, and forces our frontline cybersecurity experts to carry out critical work without pay. Based on collaboration with international partners and CISA’s forensic analysis, the ease with which these vulnerabilities can be exploited demands immediate action from all federal agencies,” said Madhu Gottumukkala, acting director of CISA.

Previous Cisco-Related Emergency Action

The directive follows earlier warnings about threats targeting Cisco systems. In September 2025, CISA issued an emergency directive warning of attackers exploiting vulnerabilities affecting Cisco Adaptive Security Appliances web services. The directive required organizations to identify all affected devices, collect forensic evidence, evaluate systems for signs of intrusion, disconnect unsupported hardware and update software to current supported releases.
Stay connected via Google News
Follow us for the latest travel updates and guides.
Add as preferred source on Google
Share5Tweet19
Previous Post

CMMC 2.0 for Small Businesses: Is It Worth It?

Next Post

Air Force, Northrop Grumman Reach Agreement to Expand B-21 Production by 25 Percent

Recommended For You

Lockheed, Navy Surface Warfare Centers Collaborate to Deploy High-Energy Laser Tech; Tyler Fitzsimmons Quoted

by Carol Collins
August 13, 2021
Lockheed, Navy Surface Warfare Centers Collaborate to Deploy High-Energy Laser Tech; Tyler Fitzsimmons Quoted

Three Naval Surface Warfare Center (NSWC) divisions have worked with Lockheed Martin to help the U.S. Navy field a laser control technology the company developed to support the branch's...

Read moreDetails

US, UK Governments Enforce New Data Access Agreement

by Naomi Cooper
October 4, 2022
US, UK Governments Enforce New Data Access Agreement

A data access agreement that enables U.S. and U.K. law enforcement to request electronic information held by telecommunications companies from the other country's jurisdictions has come into force.The...

Read moreDetails

SpaceX Launching In-Flight Abort Mission Test to Prepare for Astronaut Transportation

by Sarah Sybert
August 19, 2020
SpaceX Launching In-Flight Abort Mission Test to Prepare for Astronaut Transportation

SpaceX has announced the upcoming launch of the Crew Dragon spacecraft and Falcon 9 rocket to the International Space Station (ISS) on Jan. 18, 2019 to test the...

Read moreDetails

DHS CISO Ken Bible, Air Force CAIO Eileen Vidrine to Retire

by Naomi Cooper
April 29, 2024
Ken-Bible-and-Eileen-Vidrine_272x270

Ken Bible, chief information security officer at the Department of Homeland Security, and Eileen Vidrine, chief data and artificial intelligence officer of the U.S. Air Force, will step...

Read moreDetails

Navy Awards Penn State’s Applied Research Lab Potential $2B National Security Tech R&D Contract

by Joanna Crews
March 5, 2018
Navy Awards Penn State's Applied Research Lab Potential $2B National Security Tech R&D Contract

Pennsylvania State University's Applied Research Laboratory has received a potential 10-year, $2.11 billion contract from the Naval Sea Systems Command to research and develop technology platforms to aid U.S....

Read moreDetails
Sign Up For Our Newsletter
Subscribe to our mailing list to receives daily updates direct to your inbox!
Invalid email address
Your privacy is guranteed.
Thanks for subscribing!

Sponsors

About ExecutiveGov

ExecutiveGov, published by Executive Mosaic, is a site dedicated to the news and headlines in the federal government. ExecutiveGov serves as a news source for the hot topics and issues facing federal government departments and agencies such as Gov 2.0, cybersecurity policy, health IT, green IT and national security. We also aim to spotlight various federal government employees and interview key government executives whose impact resonates beyond their agency.

CATEGORIES

  • Acquisition & Procurement
  • Announcements
  • Articles
  • Artificial Intelligence
  • Australia
  • Awards
  • Big Data & Analytics News
  • C4ISR
  • C5ISR
  • Cloud
  • Contract Awards
  • Cybersecurity
  • Defense And Intelligence
  • Defense Security Cooperation
  • Department of War
  • DHS
  • Digital Assets
  • Digital Modernization
  • Emerging Tech
  • Events
  • Executive Moves
  • Executive Spotlights
  • Federal Civilian
  • Financial Reports
  • Foreign Military Sales
  • General News
  • GovCon Expert
  • Government Cloud
  • GSA
  • Healthcare IT
  • Industry News
  • Intelligence Community
  • Legislation
  • M&A Activity
  • Middle East
  • National Security
  • News
  • Policy Updates
  • Press Releases
  • Profiles
  • Space
  • Technology
  • Videos
  • Wash100
Sign Up For Our Newsletter
Subscribe to our mailing list to receives daily updates direct to your inbox!
Invalid email address
Your privacy is guranteed.
Thanks for subscribing!

Copyright 2026 Executive Mosaic. All Rights Reserved. Site Archive

No Result
View All Result
  • Home
  • Acquisition & Procurement
  • Agencies
    • Department of War
    • Intelligence Community
    • DHS
    • Federal Civilian
    • Space
  • Cybersecurity
  • Technology
  • News
  • About
  • Wash100
  • Contact Us
    • Advertising
    • Submit your news

Copyright 2026 Executive Mosaic. All Rights Reserved. Site Archive

Get your free GovCon news!

Get your latest GovCon news and insights. Become a VIP and subscribe to the GovConWire Daily News.

Invalid email address
We promise not to spam you. You can unsubscribe at any time.
Thanks for subscribing!